
Everything your VASP needs
Clav brings your VASP's regulatory work into one platform, from Banco Central authorization to the routine that comes after it.
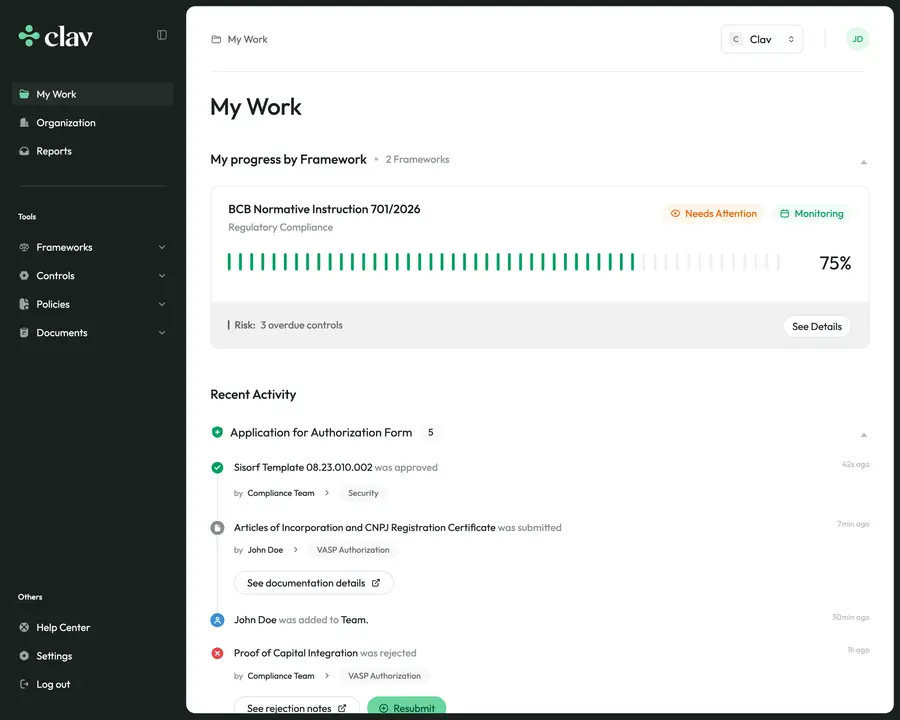
One product for each part of the regulatory work
They share the same organization, team and access controls, so you add a product without starting over.
Compliance management
Banco Central frameworks broken down into controls, requirements and evidence, each with an owner and a deadline.
- Owners, teams, deadlines and email notifications
- Evidence review with approval or change requests
- PDF reports and CSV import and export
Clav AI Assistant
Answers questions about your compliance work, reads the norms behind each requirement and reviews documents before the auditor does.
- Answers about your evidence, deadlines and review
- Reads the Banco Central norms behind each requirement
- Reviews documents, quoting the passage and the page
Wallet verification
Confirms that a self-custody wallet belongs to your customer before you send a withdrawal to it.
- Message signing on a page with your brand
- EVM networks, Bitcoin, Solana and Tron
- REST API and signed webhooks
Regulatory reports
Generates, validates and sends CCS and ACAM212 to the Banco Central, with every deadline tracked.
- Files in the layout the Banco Central expects
- Validation before each submission
- Deadline calendar and submission history
Compliance designed to operate continuously
We structure requirements, verify evidence and keep your operation's compliance running continuously.
Controls in operation
We define and organize the compliance structures applicable to your VASP operation, with clear requirements, traceable scope and well-defined regulatory base.
Regulatory Framework for Virtual Asset Service Providers
We structured and implemented a comprehensive regulatory framework for virtual asset service providers (VASPs), aligned with the requirements of the Central Bank of Brazil and international best practices.
of C-VASP Authorization Process evidence are passing
of C-VASP Authorization Process evidence are passing
Verifiable evidence
We centralize documents, tests and other compliance evidence, linking each delivery to the corresponding requirements in a verifiable way.
- CompletedRisk Management Structure (Market, Credit, Operational, Liquidity)Approved
- In ReviewCybersecurity Policy + Incident Response + Cloud Computing Service ContractingAnalyzing
- PendingAML/CFT Policy and Procedures + Internal ControlsUpload
- PendingBusiness continuity planUpload
Living policies
We monitor progress, pending items and deviations so that your operation remains in permanent compliance ready for auditing at any time.
Regulatory base
We organize and structure all the regulatory requirements of your operation in a single system, with clear scope, dependencies and continuous progress.
Tests and validations
We run automated and manual compliance tests, with approval traceability, exception management and deviation monitoring.
Clav's content and legal frameworks produced by Paiva Gomes Advogados
Co-founders: Eduardo de Paiva Gomes · Daniel de Paiva Gomes
Banco Central rules, ready to work on
Each framework arrives broken down into controls, requirements and the evidence the regulator expects, written by Paiva Gomes Advogados.
SPSAV: authorization under Resolution 520
Authorized institutions under Resolution 520
Art. 88: SPSAVs already in operation
Technical certification
Reasonable assurance report on AML controls
Ask about your compliance work and the norms behind it
Clav AI Assistant reads your frameworks, evidence, deadlines and certification review, plus the official text of the norms your frameworks cite. It answers with links to each evidence, reviews documents against their requirement and only changes something after you confirm.
Questions about your own work
What is left for me, how each framework is going, which evidence is overdue, what a colleague did this week. Every evidence in the answer is a link that opens it.
The norm behind each requirement
It reads the official text of the resolutions, normative instructions and laws your frameworks cite, article by article, and says when an article is about to change.
Document review
Compares the attached files with the requirement and the expected evidence. Findings are graded blocking, warning or informational and quote the passage and page.
Changes only after you confirm
It can fill in an information evidence, attach a link, duplicate an evidence or remember a fact for the organization. Each change shows up as a card, and nothing is written until you click Confirm.
Files stored with client-side encryption can't be reviewed, because the server can't read them.
What does the regulation say about keeping customer assets segregated?
Reading the normBCB Resolution 520/2025 covers it in a few articles:
- Art. 28: customer funds stay in individual payment or deposit accounts, apart from the provider's own
- Art. 29: the provider's own virtual assets stay apart from its customers'
- Art. 30: the segregation is set out in a policy, with proof of reserves and an independent audit
Related evidence in your framework: A.1 Asset segregation policy
Proof of who owns each self-custody wallet
Before you release a withdrawal to an external wallet, send your customer a verification link. The result is stored in Clav with the full history of the request.
Create the request
In the dashboard or through the API, enter the network, the address and your customer's ID. Clav generates a verification link.
Your customer signs
The link opens a page with your name and logo. The customer signs a message with the wallet, which costs nothing, moves nothing and gives no one access to the wallet.
The wallet is verified
The address shows up as verified in Clav, with every attempt recorded. Your systems receive a signed webhook.
Supported networks
- Ethereum
- Polygon
- Arbitrum
- Optimism
- Base
- BNB Smart Chain
- Avalanche
- Bitcoin
- Solana
- Tron
Mainnet only. Test networks are rejected.
How your customer can prove ownership
- Wallet connection via WalletConnect
- Manual signature, for hardware wallets and command-line tools
- Bitcoin micro-transaction, from 546 to 2,000 sats
- REST API with a dedicated token scope
CCS and ACAM212 generated, validated and sent by Clav
Each file comes from your VASP's own data, and every deadline shows up on a calendar. The reports live next to the rest of your compliance work, with the same team and access controls.
Choose how it runs: on your infrastructure or managed by ClavFiles ready in the right layout
Clav builds each file from your VASP's customer and transaction data, in the format the Banco Central expects.
Checked before it goes out
Errors and inconsistencies show up before submission, while there is still time to fix them.
Sent from Clav
The validated file goes to the Banco Central without leaving the platform, and every submission stays in the history.
Deadlines in one calendar
The team sees what is due and when, gets reminders before each deadline and can look up everything already sent.
- Regulation
- Resolução BCB 179/2022
- Frequency
- Whenever a customer relationship starts or ends
- Regulation
- IN BCB 693/2025
- Frequency
- Monthly, by the 5th of the following month
- Delivery
- XML file through the STA
Built for regulated data
Controls your security team usually asks about when assessing a vendor.
Client-side encryption
Optional. Files are encrypted in the browser with AES-256-GCM before upload, so the server stores content it can't read.
SSO with SAML and OIDC
Connect your identity provider and require SSO for every member of the organization.
Two-factor authentication
Authenticator app with backup codes. Administrators can make it mandatory for the whole organization.
Audit log
Changes to keys, members, SSO and security settings are recorded along with who made them.
API with scoped tokens
REST API with per-scope tokens, rate limiting and an access log, documented in OpenAPI.
Portal for auditors
Audit firms get their own portal to read evidence and approve it or request changes, only in the organizations they certify.
Technical foundations of Clav
A technical overview of how Clav ensures security, compliance and data integrity in regulated operations.
Transparency and audit
We believe in transparency. Our technical documentation is publicly available so you can understand exactly how we protect your data and maintain compliance.
See all documentationLatest articles
- BCB NI 739 in Phase 2: how an operating SPSAV prepares for reasonable assuranceAn SPSAV that was already operating files the AML/CFT reasonable assurance report in Phase 2, within 60 days of the Central Bank's decision on Phase 1. See how limited and reasonable assurance differ, the 38 points of Annex IV and why the work has to start earlier.
- What is a PSAV: Brazil's definition of a virtual asset service provider (VASP)PSAV is the Brazilian term for a virtual asset service provider. See the definition in Law 14,478/2022, the difference between PSAV, SPSAV and VASP, who can be a PSAV and what the Banco Central requires.
- BCB Resolution 520: a guide to VASP regulation and Banco Central authorization in BrazilWhat BCB Resolution 520/2025 requires from crypto exchanges and virtual asset service providers in Brazil: SPSAV types, Banco Central authorization, asset segregation, custody and the 2026 deadlines.
Frequently asked questions
Compliance management for Banco Central frameworks, Clav AI Assistant for questions about your work, the norms behind each requirement and document review, and verification that a self-custody wallet belongs to your customer. Clav also generates and sends CCS and ACAM212 to the Banco Central. Everything runs on the same account, with the same team and access controls.
It builds the CCS and ACAM212 files from your VASP's data, validates them before submission, sends them to the Banco Central and tracks each deadline. ACAM212 is the monthly C212 document set by IN BCB 693/2025, due by the 5th of the following month.
What is left for you, how each framework is going, which evidence is overdue, what the auditor asked and what a norm cited by your framework says. It answers with links to each evidence and the article it relies on, and any change it proposes waits for your confirmation.
It compares the attached files with the requirement and the expected evidence and lists what is missing or inconsistent. Each finding quotes the passage and the page it relies on, and your team decides whether to apply it.
No. With client-side encryption on, the server can't read the document, so the review isn't available for those files. Files kept in the default storage mode can be reviewed.
Ethereum, Polygon, Arbitrum, Optimism, Base, BNB Smart Chain, Avalanche, Bitcoin, Solana and Tron, on mainnet. Your customer can sign through WalletConnect or paste a signature made elsewhere, and on Bitcoin there is also a micro-transaction option.
No. Signing a message costs nothing, moves no funds and gives no one access to the wallet.
With evidence continuously collected and organized, your company is always ready for audits. No more scrambling to gather documents at the last minute.
One account for all of your VASP's regulatory work
Request access and tell us which products your operation needs. We turn on the ones you choose.